
Cryptographic Hash Perform Glossary Csrc
Hashing is the method of changing data—text, numbers, information, and virtually something else—into a set number of bytes (represented by a string of seemingly random letters and numbers). This is completed by way of a specialized mathematical algorithm known as a hash perform. Information integrity checks, generally utilizing hash capabilities, provide assurances in regards to the accuracy of data recordsdata by creating checksums. This methodology allows users to detect any alterations made to the unique file. SHA1 was developed by the US Nationwide Safety Agency (NSA) and is similar to MD5. It generates 160-bit hash values, represented by 40-digit long https://www.360-expeditions.com/expeditions/mount-kenya-trek/ hexadecimal strings.
Collision Resistance
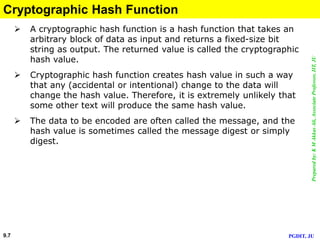
CityHash is another non-cryptographic hash operate that is designed for quick hashing of huge quantities of information. It is optimized for contemporary processors and offers good efficiency on both 32-bit and 64-bit architectures. A hash perform in cryptography is type of a mathematical perform that takes various inputs, like messages or knowledge, and transforms them into fixed-length strings of characters. Means the input to the hash operate is of any length but output is all the time of fastened length. For every block of input information, the hash function updates the interior state using a combination of bitwise operations, modular arithmetic, and logical transformations. These operations are performed iteratively, and the process ensures that even small changes within the input lead to vastly different hash outputs (the Avalanche effect).
Digest And Safety Properties
- Collision resistance makes it exhausting to search out any two different messages with the same digest.
- It offers an different selection to SHA2 and can be used for safe hashing.
- For a number of years, MD5 was the preferred and sometimes used hash operate.
- These are computational properties with an assumed safety energy.
Asymmetric encryption is much slower than symmetric encryption, however in phrases of being safe it excels! Asymmetric encryption generates a pair of keys, a public key, and a non-public key. The public key may be shared, but your non-public key should be saved by you in a secure location. Symmetric encryption generates a single key, that encrypts and decrypts (turns ciphertext into plaintext). For instance, let us say we’ve a Microsoft word document we need to send to our boss.
Password Authentication
Hashing involves converting a data set of any measurement right into a shorter, fixed-length output using a mathematical formulation. When the information is received, the recipient recalculates the checksum using the identical methodology. If the new checksum matches the original one, it’s probably that the message was transmitted with out errors. Whereas CRC is efficient for error detection, it is not a security measure. It is primarily used to ensure the integrity of information during transmission, not to defend it from unauthorized access or modification. The significance of this process lies in its era of a novel “fingerprint” for every input.
The four SHA algorithms which make up the SHA household are SHA-0, SHA-1, SHA-2, and SHA-3. Hashing operations occur rapidly, even for giant amounts of knowledge sets. In this blog publish, we’ll explore the rules and sensible functions of hashing. Ambiguous serialization can let two components assign totally different which means to the same bytes or totally different bytes to the same logical object. Embrace function, version, algorithm, and related context when one digest development serves a quantity of domains.
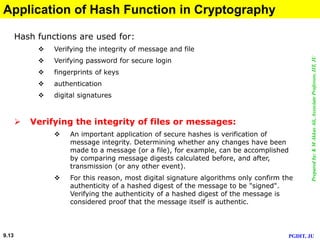
This ensures that plaintext passwords are not saved and helps defend towards unauthorized entry. Instead of storing passwords in clear, mostly all login processes retailer the hash values of passwords in the file. In computing techniques, hash features are frequently used information constructions for duties like info authentication and message integrity checks. They aren’t easily decipherable, but because they are often solved in polynomial time, they are considered cryptographically “weak”. Our focus on this article is principally on “cryptographic hashing,” which refers to hashing capabilities designed to strengthen security measures.
Think of this as a digital key that may lock, unlock, or a mixture of both. Encryption could be damaged down into two classes, symmetric and asymmetric. Digital signatures employ CHFs to verify the authenticity and integrity of a message or doc. A signer generates a hash of the message, indicators it with their personal key, after which the recipient verifies the signature with the signer’s public key before evaluating the hash values for consistency.